What your audit will ask for.
Easycore's regulatory posture, our governance documents in open access, and the people to write to. For compliance teams, DPOs and CISOs.
The posture, in four frameworks.
Each framework, and how Easycore answers it by design.
AI ActRegulation (EU) 2024/1689
Outside high risk, by design.
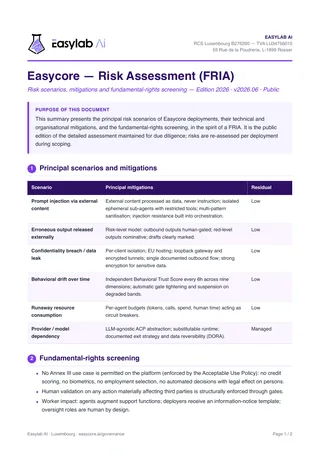
General-purpose system: no credit scoring, no biometrics, no automated decision with legal effect. No Annex III use case is permitted on the platform.
DORARegulation (EU) 2022/2554
Structured as a third-party ICT provider.
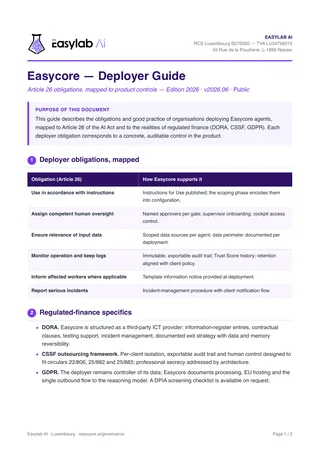
For financial entities: register of information, clauses, testing, incident management, exit strategy.
GDPRRegulation (EU) 2016/679
Hosted in the EU, one machine per agent.
Dedicated machines, data minimisation. Reading memory involves no third-party model.
CSSF professional secrecyCirculars 22/806, 25/882, 25/883
Addressed by architecture.
A dedicated machine per agent, exportable audit log, outsourcing framework respected.
Four dossiers to go deep.
The hub summarises. The dossiers demonstrate.
- SecurityIsolation, encryption, sealed audit log, access management, hosting.Open
- Governance and AI ActThe six governance documents in context, and the regulatory posture article by article.Open
- Memory and sovereigntyHow your agents' memory is built, where it lives, how you get it back.Open
- ArchitectureThree isolated zones, three-layer transport, encryption, data, compliance and maturity, principle by principle.Open
Your due diligence file, already written.
The six governance documents are in open access, no form to fill in. The detailed architecture file is handed over on request, as part of a due diligence.
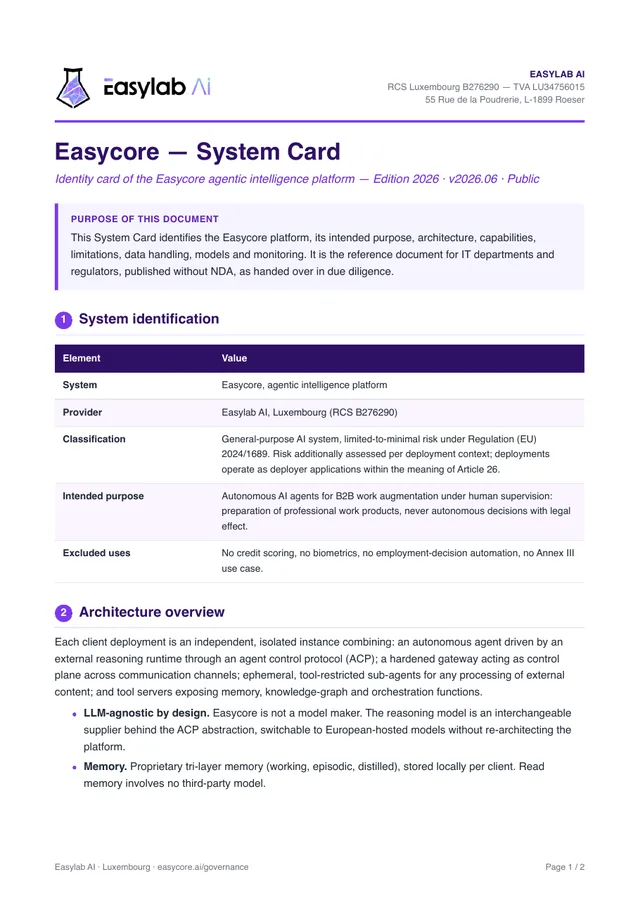
2026 edition, v2026.06
System Card
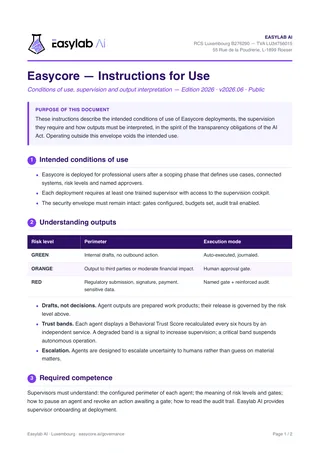
The platform's identity card: intended purpose, architecture, capabilities, limitations, data, models, monitoring. The reference document for your IT department and your regulator.
PDF, 98 KB
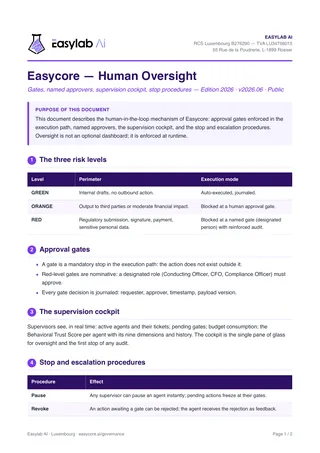
The six governance documents
For your committee, your CISO review or your outsourcing questionnaire. In open access, no NDA.
Direct download, PDF in English
Request the architecture file
The detailed architecture file (topology, transport, cryptographic primitives, article-by-article mappings) is confidential. We hand it over as part of a due diligence, and we talk your questions through with your team.
What you verify yourself.
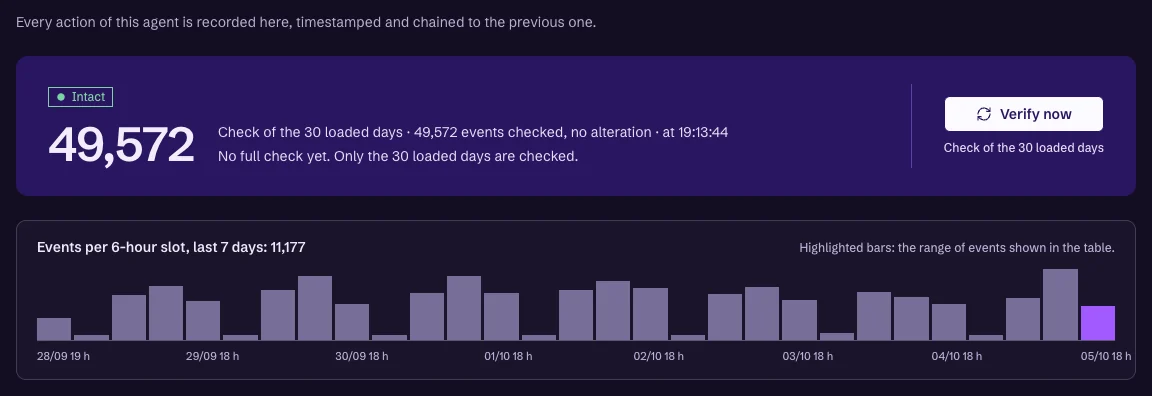
The sealed audit chain
Every action is timestamped, hashed and chained to the previous one. You verify the chain from the cockpit and export it for your regulator.
The trust score
Computed by code across eight dimensions: seven measured on the agent's real sessions, the eighth (the integrity of its audit chain) checked by the trust service. The agent never scores itself.
Live supervision
In the cockpit: each agent's activity, its memory, its score, in real time.

Who to write to.
Direct addresses, read by people.
- Data Protection OfficerJulien Doussotdpo@easylab.ai
- Compliancecompliance@easylab.ai
- Personal dataprivacy@easylab.ai
- Legal questionslegal@easylab.ai
Talk to our CTO.
Philippe Hougardy. Thirty minutes on your outsourcing framework, your DORA register and your architecture questions.
Request a call