Our governance documents, openly available.
Six documents, exactly as we hand them over in due diligence: no NDA, no form, one click to download.
- edition
- 2026
- version
- v2026.06
- language
- English
- file
- PDF, 2 pages, 98 KB
The six documents.
2026 edition, version v2026.06, written in English. They describe the platform as of the edition date.
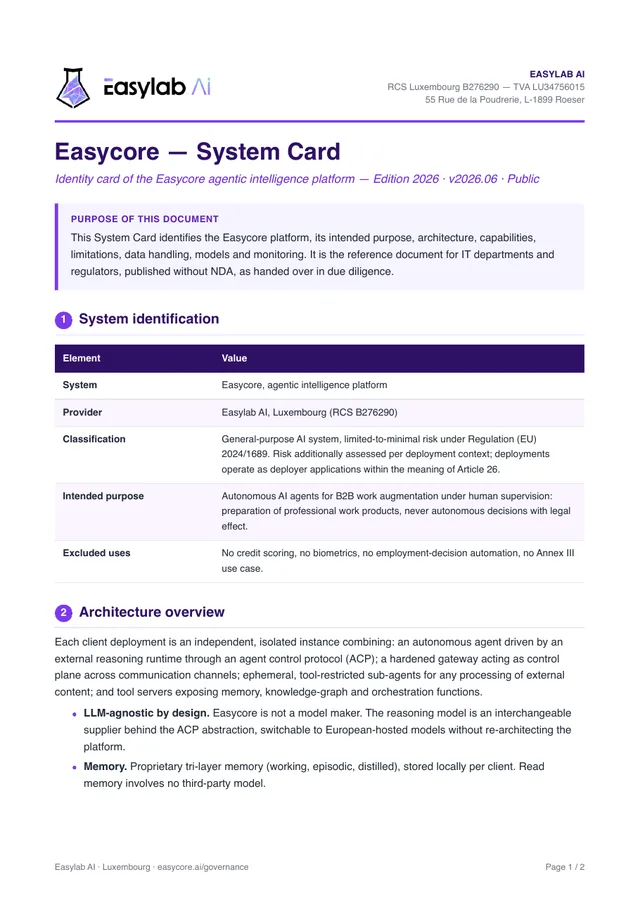 Download System Card
System Card
The system's identity card: classification, intended purpose, architecture, capabilities and limitations, data, monitoring. The reference for your IT department and your regulator.
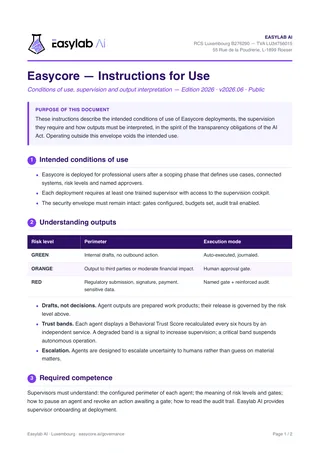 Download Instructions for Use
Instructions for Use
The intended conditions of use, how to read the agent's outputs, and the competence expected from those who run it.
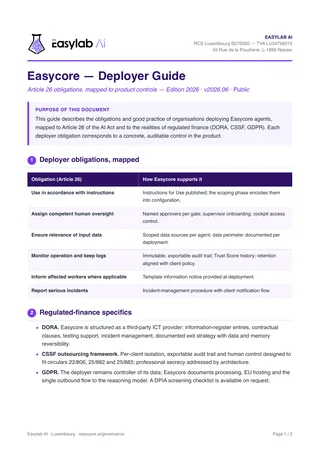 Download Deployer Guide
Deployer Guide
Deployer obligations (Article 26 of the AI Act), each mapped to a product control, followed by the DORA, CSSF and GDPR points.
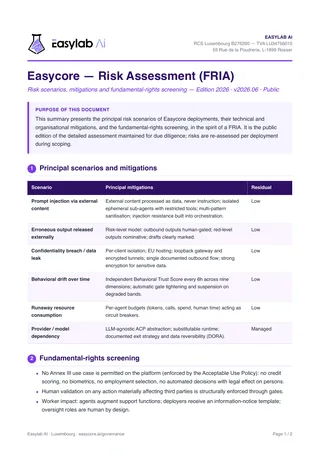 Download Risk Assessment (FRIA)
Risk Assessment (FRIA)
The principal risk scenarios, their mitigations and the fundamental-rights screening.
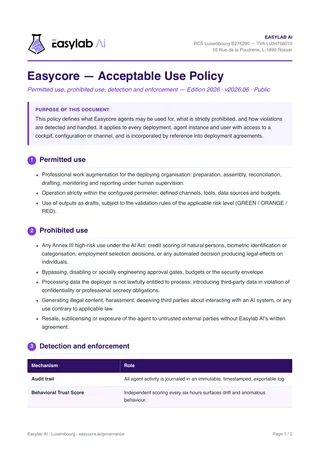 Download Acceptable Use Policy
Acceptable Use Policy
What agents may be used for, what is prohibited, and how violations are detected and handled.
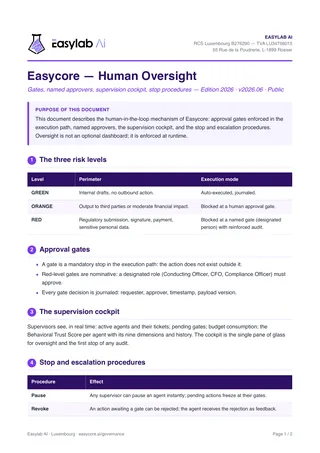 Download Human Oversight
Human Oversight
The oversight mechanism: risk levels, cockpit, stop and escalation procedures.
The framework, plainly.
What these documents say, in three points.
- AI Act
- A general-purpose AI system, limited-to-minimal risk under Regulation (EU) 2024/1689, and reassessed for each deployment. No Annex III use case is permitted: no credit scoring, no biometrics, no employment selection, no automated decision with legal effect on a person.
- Article 26
- Every deployer obligation is mapped to an element of the product or the documents: published instructions, a sealed and exportable audit trail, trust score history, a template worker information notice, an incident-management procedure.
- GDPR
- The deployer remains the controller. Data minimisation by design, a dedicated machine per agent, memory stored on that machine. Outbound flows are encrypted and documented: the reasoning model, plus memory embedding in a standard installation; a sovereign installation blocks everything else. A DPIA screening checklist is available on request.
For regulated finance, Easycore is structured as a third-party ICT provider under DORA (information register, incident management, exit strategy with data and memory reversibility); its dedicated machine per agent and exportable audit trail are designed for the CSSF outsourcing framework (circulars 22/806, 25/882 and 25/883).
These documents describe compliance by design, as the platform stands at the edition date. They do not constitute legal advice. This framework sits within Easylab AI's own: group governance.